
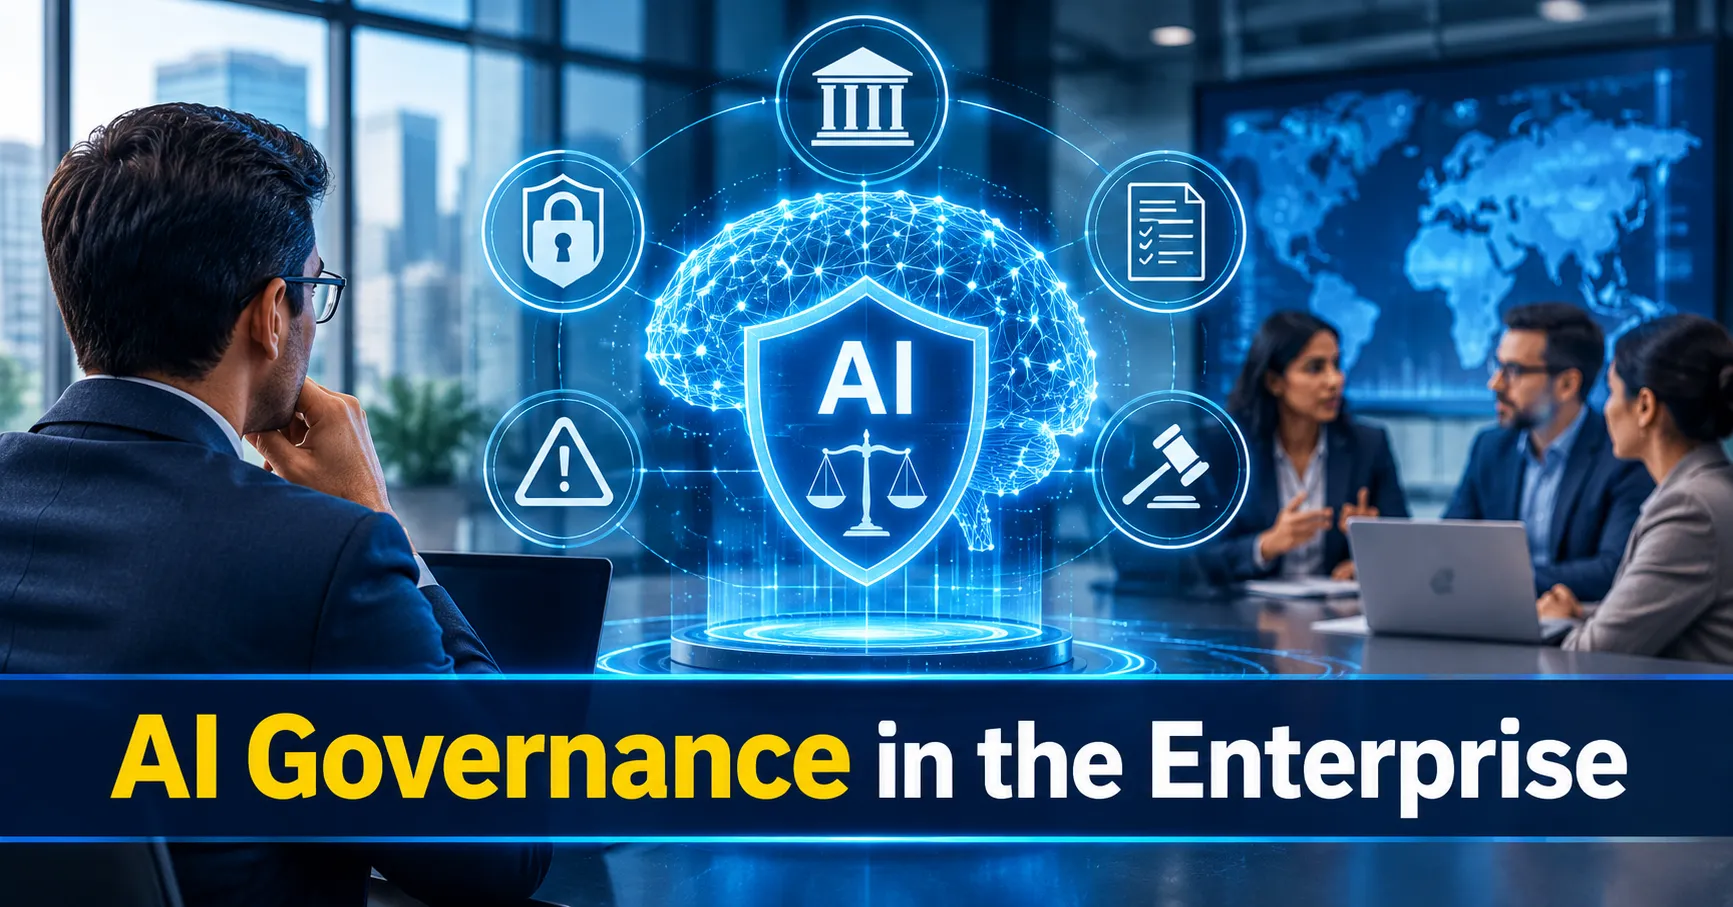

Every company is shipping AI models right now. Chatbots, fraud detectors, recommendation engines, agentic workflows. But here’s the kicker, four out of five enterprise AI deployments don’t even have a named owner. No owner, no accountability, and that’s a ticking time bomb when regulators come knocking.
AI governance ain’t a checkbox anymore. It’s the difference between scaling responsibly and catching fines up to €35 million or 7% of global turnover under the EU AI Act.
Rules Got Teeth in 2026
The regulatory game changed big time in 2026. The EU AI Act’s transparency obligations went live in August, and the Digital Omnibus gave orgs a little more runway by pushing high-risk obligations to December 2027. The NIST AI RMF is holding it down as the US federal baseline, and ISO/IEC 42001 is the certifiable international standard everybody’s pointing to. Most enterprises are stacking all three into one layered framework, and honestly, that combo is lowkey the gold standard right now. The SEC also pulled up with a dedicated SOX enforcement group in March 2026, so AI-driven financial decisions are catching major heat. If AI is touching people, money, or compliance, governance ain’t optional no more, it’s deadass mandatory.
Responsible AI, Broken Down
Six principles running the whole show: Fairness, Transparency, Accountability, Safety, Privacy, and Human Oversight.
Fairness means bias detection lives inside the model lifecycle, not bolted on like some last-minute band-aid
Transparency means keeping the receipts clean, documentation a regulator can actually verify without breaking a sweat
Accountability means every AI system got a named owner and escalation paths that are crystal clear
Safety means going hard on defense against prompt injection, model theft, and data poisoning
Privacy means data governance built from the ground up, not some Frankenstein setup thrown together after the fact
Human Oversight means humans call the shots on high-risk decisions, no autopilot, no exceptions
Orgs with formal governance frameworks are slashing regulatory risk by 60-80%. That stat hits differently when the board starts asking questions.
Access Controls and Auditability
RBAC for AI agents is the policy layer deciding which roles can spawn which agents, with which permissions, on which data. Both GDPR Article 30 and the EU AI Act require this level of granularity now.
On the audit side, Article 12 requires high-risk AI systems to automatically record events over the system’s entire lifetime. Article 26 mandates log retention for at least six months so decisions can be reconstructed. If it’s not logged, it didn’t happen.
Risk Management That Scales
The NIST AI RMF gives orgs four functions to work with, Govern to set the rules, Map to find the risks, Measure to quantify the exposure, Manage to lock it down, and that loop is what separates companies scaling AI responsibly from the ones just winging it. Governance as a competitive advantage, not a compliance headache, that’s the whole move right now.
For enterprises looking to get AI governance right without slowing down innovation, Tetrahed.com delivers the strategy, the frameworks, and the technical execution to make compliance a competitive advantage instead of a bottleneck.
Join the conversation