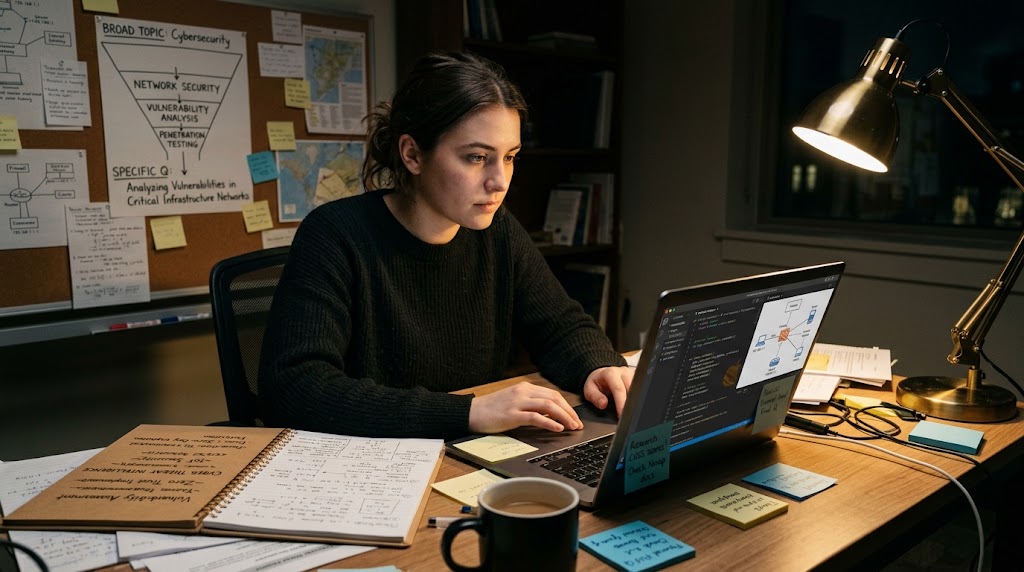
A student once showed me a dissertation proposal titled “Cybersecurity in the Age of AI.” Six words, and somehow every single one of them was doing too much work. It wasn’t a bad idea, exactly. It was a hundred bad ideas stacked on top of each other, none of them visible yet because the whole thing was still wrapped in fog. That’s the trap almost everyone falls into at the start, and it has nothing to do with intelligence or effort. It’s a scoping problem, and scoping is a skill nobody actually teaches you until you’re already stuck.
Cybersecurity makes this worse than most subjects, because nearly everything in it sounds like a legitimate research area on first hearing. Phishing, ransomware, insider threats, cloud misconfiguration say any of these out loud in a supervision meeting and nobody blinks, because they’re all real and all important. The trouble is that each one is a domain containing dozens of narrower, genuinely answerable questions, and mistaking the domain for the question is the single most common reason students stall for weeks before writing a proper word of their proposal.
Why the Obvious Starting Point Falls Apart
The natural instinct is to think of a threat you’ve read about in the news and start there. It feels productive, because the subject is current and clearly matters. But importance and researchability are two different things, and conflating them is where most proposals quietly go wrong before anyone notices.
A workable question needs edges. It needs a defined group of people or systems, a specific mechanism, something measurable, or a comparison between two stated conditions. “Cloud security” has none of that on its own it only becomes usable once it’s cut down to something like misconfigured access permissions in one particular type of storage platform, examined under one particular set of conditions. The subject hasn’t changed. The scope has. That sentence looks tidy on a page; it rarely feels tidy at midnight, staring at a blank document with a deadline circled in red.
Some students resist narrowing because a smaller question feels less impressive, almost embarrassing to hand in. I understand the instinct, but it’s backwards. Nobody marking your dissertation is grading how frightening your chosen threat sounds. They’re grading whether you designed a study, carried it through properly, and reached something defensible at the end. A precise question, done well, beats a sweeping one done vaguely almost every time and the gap between those two outcomes is usually bigger than students expect going in.
Turning a General Concern Into a Specific Question
The real shift is moving from “what’s interesting about this” to “what’s still genuinely unresolved about this.” Interest gets you in the door. It doesn’t get you a research question, because most broad cybersecurity concerns already have plenty written about them in general terms. What’s usually missing is examination under one particular condition, population, or constraint that hasn’t been looked at properly yet.
Take phishing, since almost every student considers it at some point. Everyone already accepts it’s a persistent problem, which is precisely why “raising phishing awareness” makes a weak topic it’s been said so many times it no longer invites a new finding. A sharper version might ask why certain phishing detection training methods fail specifically among staff who’ve already completed earlier awareness training. That’s a different question entirely. It has a defined group, a specific failure point, and something worth actually measuring, rather than restating.
Testing Whether an Idea Can Actually Be Researched
Before committing to a direction, question it the way your supervisor eventually will, out loud, in front of you. Can it realistically be answered using tools a student can access surveys, existing public datasets, a small controlled test environment or does it quietly depend on incident data or organisational access nobody is going to hand over? A topic that sounds compelling but relies on information you’ll never obtain isn’t really a topic. It’s a wish with good branding.
It also helps to ask whether the question could reasonably be answered more than one way. If there’s only one obvious answer, you’re not really researching anything. “Is multi-factor authentication more secure than a password alone” isn’t a research question, it’s a settled fact wearing a question mark for effect. A better version asks something the existing literature hasn’t pinned down why adoption of multi-factor authentication stays patchy among a specific group despite the well-documented benefits, for instance. That version has friction to it, and friction is more or less what research exists to work through.
Where Strong Ideas Actually Come From
Good ideas rarely arrive as a subject lifted straight from a headline. They tend to surface from a contradiction noticed mid-read, from a gap a paper’s own authors admit to in their limitations section, or from something a student has noticed directly a mismatch between what a workplace security policy says on paper and what people actually do when nobody’s checking. That last one is worth taking seriously; it’s where some of the more honest, useful cybersecurity research topics tend to start, because they’re rooted in something the student has genuinely observed rather than borrowed from someone else’s headline.
Reading the “limitations” and “future work” sections of published papers is one of the most underused habits I know of. Researchers often mention, almost in passing, what they didn’t have time or access to examine properly. That passing comment can be a fully formed opening for somebody else’s dissertation, just sitting there, unclaimed, while most students skip straight to the conclusion looking for a neat summary instead.
Here’s the part that’s easy to miss entirely: a strong topic doesn’t need to be new in subject matter, only in angle. Insider threat detection has been studied about as thoroughly as anything in the field, yet examining it within a specific setting hospital shift workers with irregular system access, say, rather than office staff on a nine-to-five can still produce something genuinely worth writing, because the underlying behaviour patterns differ enough to matter.
Narrowing Without Losing the Point
There’s a failure on the other side too, and it gets mentioned far less often. Narrow too hard and the topic turns trivial technically answerable, but teaching nobody anything beyond the one case sitting in front of you. I’ve watched students overcorrect after being told their first idea was too broad, ending up with something so tight it barely connects to anything a reader would recognise as significant. The fix isn’t always to narrow further. Sometimes it’s to narrow in a different direction entirely.
A properly scoped topic tends to do three things at once: it’s small enough to investigate with the time and access actually available, it still connects to a concern people would recognise as genuinely important, and answering it would plausibly change how someone thinks or acts, even a little. Miss any one of those and the honest response is to reframe, not to abandon the subject the subject was probably fine all along. It was the shape of the question that needed work.
The Real Skill Being Tested
Most guidance on this subject stops right at the point where the real difficulty actually begins, which is a shame, because that’s exactly where students need the most help. Choosing well was never about finding the most alarming threat to write about. It’s about proving you can take something large and genuinely uncertain and cut it down to a question you can actually answer with the time and tools you have and that skill matters to examiners more than the subject matter itself ever will.
I won’t pretend there’s a clean formula for knowing the moment a topic is narrow enough. I’ve got it wrong myself, on both sides once too broad, and once, memorably, so narrow there was barely anything left worth saying. The best test I’ve found is simple: if you can’t roughly picture what your findings section might say, the question isn’t there yet. Keep cutting until you can see it.